Network security is no longer about building a strong wall around a company’s internal network. Businesses now operate across cloud platforms, remote workplaces, mobile devices, third-party applications, and distributed systems. Employees may access company resources from almost anywhere, while applications and data can exist across multiple environments.
This changing digital landscape has made traditional perimeter-based security harder to manage.
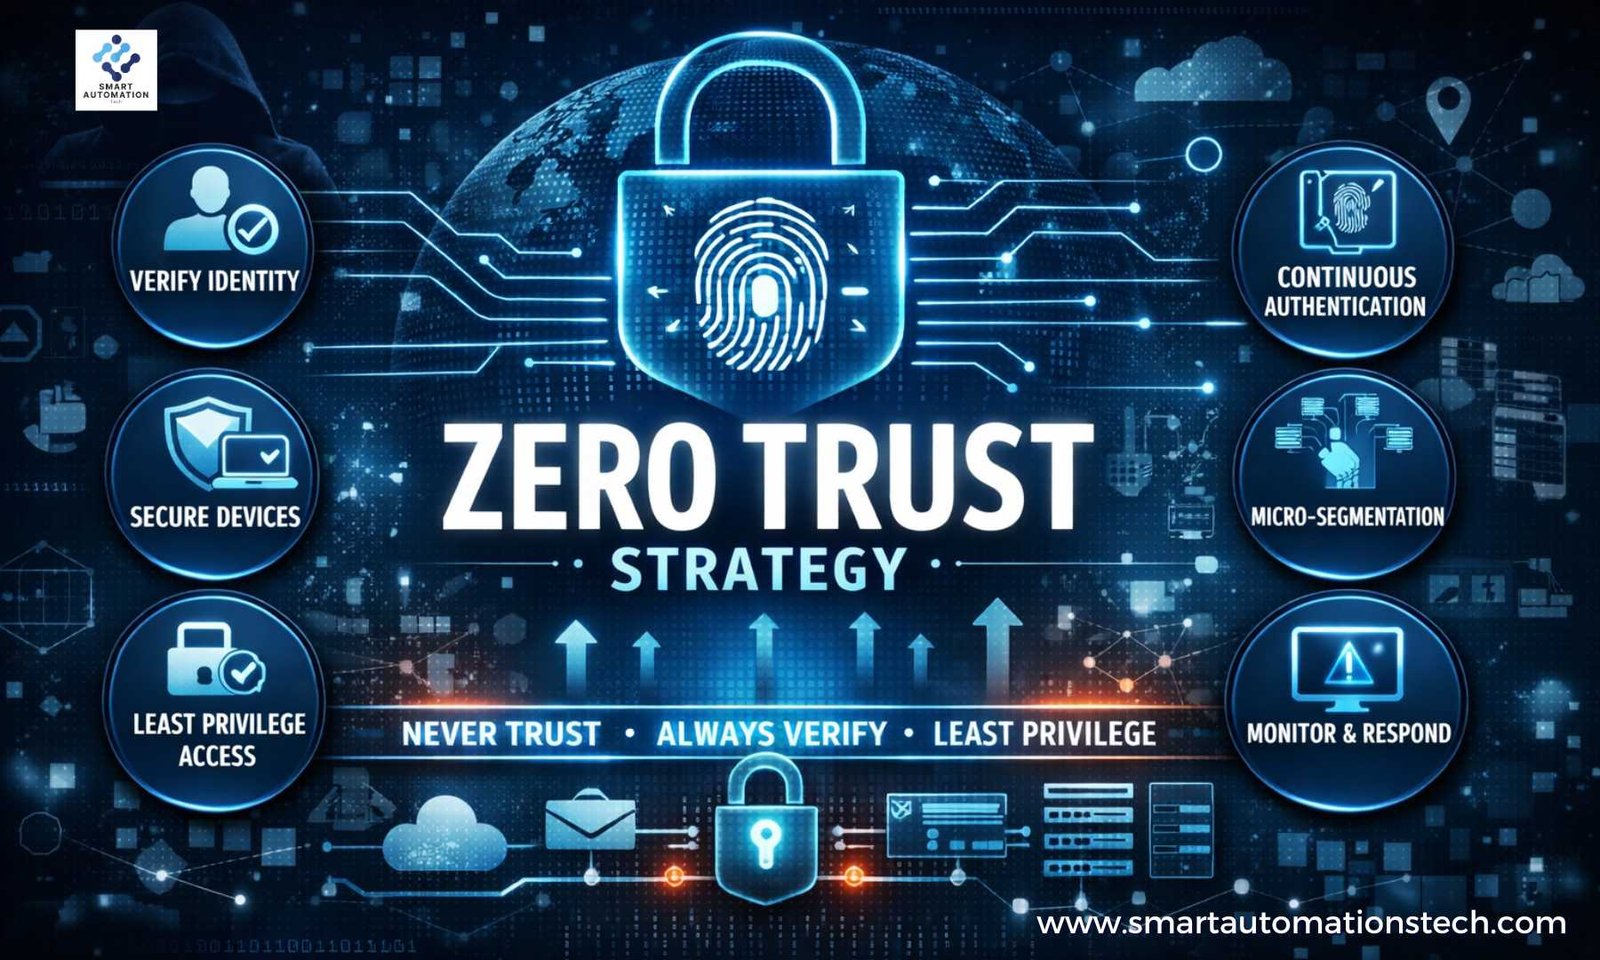
A Zero Trust Strategy offers a different approach. Instead of assuming that a user or device is safe simply because it is connected to a trusted network, Zero Trust requires access to be verified before a resource is made available. NIST describes this model as removing implicit trust based on physical or network location and focusing protection on users, assets, and resources.
The result is a more focused approach to network access control—one that can help organizations reduce unnecessary access and limit the damage caused by compromised accounts or devices.
What Is a Zero Trust Strategy?
A Zero Trust Strategy is a cybersecurity approach built around a simple principle: trust should not be automatically granted.
Every request to access a system, application, database, or other resource should be evaluated based on identity, permissions, device condition, context, and security policy.
For example, imagine an employee who normally accesses a company’s customer management platform from a company-managed laptop. If that employee’s credentials are suddenly used from an unfamiliar device to access sensitive customer information, the security system can treat the request differently.
It may ask for additional authentication, restrict access, or block the request altogether.
This makes network access more dynamic and security-focused.
Why Traditional Network Access Control Is No Longer Enough
Traditional security models were largely designed around a clear network perimeter. A firewall could protect the boundary, while users inside the network were often given relatively broad access.
That model becomes more difficult when employees work remotely and organizations rely heavily on cloud services.
A compromised account can also become a serious problem if being inside the network provides access to many additional resources.
NIST notes that traditional perimeter defenses are less effective against threats involving remote workers, cloud-based services, and internal lateral movement.
Zero Trust addresses this problem by shifting attention from where a connection comes from to who or what is requesting access and what resource they need.
How Zero Trust Changes Network Access Control
1. Identity Comes First
Identity is at the center of modern Zero Trust access control.
Instead of relying mainly on network location, organizations can verify the identity of users, applications, and devices before allowing access.
Multi-factor authentication can add another layer of protection by requiring users to provide more than a password.
This becomes particularly important when employees access business systems from different locations and devices.
2. Least-Privilege Access Reduces Risk
Zero Trust does not mean giving users access to everything after authentication.
The principle of least privilege means users should receive only the permissions necessary for their work.
For example, a content writer may need access to a content management platform but may not need access to financial systems or sensitive employee records.
Reducing unnecessary permissions can limit what an attacker can reach if an account is compromised.
3. Devices Must Also Be Trusted Carefully
A legitimate user does not automatically mean that the device being used is secure.
A Zero Trust environment can evaluate device conditions before granting access. Security policies may consider whether the device is managed, updated, encrypted, or meeting organizational security requirements.
If a device presents a significant security risk, access can be restricted even when the user’s credentials are correct.
4. Access Depends on Context
Zero Trust can evaluate more than usernames and passwords.
An access decision may consider:
- User identity
- Device status
- Requested application
- Resource sensitivity
- Location
- Time
- Authentication strength
- Current risk signals
- User permissions
This allows organizations to make more precise access decisions instead of treating every request in exactly the same way.
5. Continuous Verification Becomes Important
Authentication should not necessarily be treated as a one-time event.
A user’s risk profile can change during a session. For example, unusual activity, a sudden change in device behavior, or an attempt to access a highly sensitive resource may trigger additional security controls.
Continuous evaluation can help security teams respond when normal behavior changes.
Zero Trust and Cloud Security
Cloud computing has significantly changed the way businesses build and operate their technology environments.
Applications and databases may be distributed across different cloud providers, private infrastructure, and SaaS platforms. Employees may also access these services without ever connecting to a traditional corporate network.
A Zero Trust Strategy works well with this environment because it focuses on protecting individual resources rather than assuming that everything within one network boundary is trustworthy.
NIST’s cloud-native Zero Trust guidance also emphasizes moving access control toward identity-based policies for users, applications, and services across multi-cloud environments.
This can help organizations apply more consistent security policies across modern infrastructure.
The Role of Multi-Factor Authentication
Passwords remain one of the weakest points in many security environments.
Even strong passwords can be stolen through phishing, credential leaks, malware, or social engineering.
Multi-factor authentication makes unauthorized access more difficult by requiring an additional verification factor.
For example, a user may need to provide a password and approve a login through an authentication application.
MFA alone is not a complete Zero Trust Strategy, but it can become an important component of a broader identity and access-control framework.
Zero Trust Helps Limit Lateral Movement
One of the biggest concerns after a successful breach is lateral movement.
An attacker who compromises one account or device may attempt to move through the environment and discover additional systems.
Traditional network models can make this easier when internal access is broad.
Zero Trust reduces the opportunity for unrestricted movement by applying more granular access policies. A user or compromised device may be allowed to access one resource while being prevented from reaching unrelated systems.
This creates smaller trust boundaries and can reduce the potential impact of a security incident.
Zero Trust and Remote Employees
Remote work has made traditional network boundaries less meaningful.
Employees can work from homes, coworking spaces, hotels, or other locations. They may also use multiple devices and cloud-based applications during the same working day.
A Zero Trust model allows organizations to focus on the individual access request instead of assuming that a particular physical location represents a trusted environment.
This makes security policies more adaptable to modern working conditions.
Zero Trust and Third-Party Access
Businesses often work with contractors, vendors, consultants, and technology partners.
Giving these external users broad network access can create unnecessary security exposure.
With Zero Trust principles, organizations can provide access only to the applications or resources required for a specific task.
For example, a contractor working on a particular application may receive access to that application without gaining access to unrelated internal systems.
This creates a more controlled relationship between external users and business resources.
How Automation Strengthens Zero Trust
Managing thousands of access requests manually would be impractical.
Automation can help security teams enforce policies consistently and respond quickly to changing conditions.
For example, an automated system could identify unusual login activity and request additional authentication. It could also restrict access when a device fails security requirements or when a user attempts to reach a resource outside their normal permissions.
AI and analytics can further support security teams by identifying unusual patterns across large volumes of activity.
However, automation should support carefully designed security policies rather than replace human oversight completely.
Key Benefits of a Zero Trust Strategy
A well-planned Zero Trust approach can provide several important advantages.
Stronger Access Control
Organizations gain greater control over who can access specific resources.
Reduced Attack Surface
Limiting unnecessary permissions can reduce the number of systems available to compromised accounts.
Better Cloud Protection
Identity-based policies can help protect applications and services across hybrid and multi-cloud environments.
Improved Remote Security
Employees can securely access business resources without relying entirely on a traditional corporate network perimeter.
Greater Visibility
Security teams can gain better insight into users, devices, applications, and access activity.
Better Containment
If an account or device is compromised, granular access controls can help limit how far the attacker can move.
Challenges of Implementing Zero Trust
Although Zero Trust offers significant security benefits, implementation requires careful planning.
Many organizations have older applications that were not designed for modern identity-based access controls. Integrating these systems can take time.
Another challenge is understanding existing permissions. Businesses may discover that users have accumulated access over several years without a clear business reason for retaining it.
There is also a user-experience challenge. If security policies create excessive authentication requests or unnecessary restrictions, employees may become frustrated.
For this reason, Zero Trust should be implemented gradually and based on business requirements.
A Practical Approach to Zero Trust Implementation
Organizations do not need to transform their entire infrastructure overnight.
A practical starting point is to identify the most important applications, data, and systems.
Next, organizations can determine who currently has access to those resources and whether that access is actually required.
From there, businesses can strengthen identity verification, introduce multi-factor authentication, review permissions, improve device security, and establish more granular access policies.
Monitoring should then be used to identify unusual behavior and improve security policies over time.
This staged approach can make Zero Trust easier to manage while allowing security teams to measure progress.
The Future of Network Access Control
The future of network security is moving away from the idea that everything inside a corporate network can automatically be trusted.
Cloud computing, remote work, connected devices, APIs, and distributed applications have created environments where a traditional network perimeter is no longer enough.
A Zero Trust Strategy changes the focus from simply protecting the network to protecting individual resources and controlling access to them.
NIST’s Zero Trust work describes this shift as moving defenses from static network-based perimeters toward users, assets, and resources.
As organizations continue adopting distributed technology, this approach will become increasingly important for managing access securely.
Conclusion
Network access control is undergoing a major transformation.
The traditional model of trusting users because they are inside a corporate network does not fit today’s highly connected business environment. Employees, applications, devices, and data can exist in many different locations, creating new opportunities for attackers.
A Zero Trust Strategy responds to these challenges by requiring access to be verified, limiting permissions through least privilege, evaluating devices and context, and continuously monitoring security conditions.
Zero Trust is not simply another security product. It is a broader way of thinking about access.
By focusing on identity, resource protection, continuous verification, and controlled permissions, organizations can build a stronger security foundation for the modern digital workplace.
Frequently Asked Questions
1. What is a Zero Trust Strategy?
A Zero Trust Strategy is a security approach that does not automatically trust users or devices. Every access request is verified based on identity, permissions, device condition, and security requirements.
2. How does Zero Trust improve network access control?
Zero Trust improves access control by giving users only the permissions they need. Identity verification, least-privilege access, device checks, and monitoring help reduce unnecessary access.
3. Is Zero Trust useful for remote employees?
Yes. Zero Trust can protect remote employees by evaluating identity, device security, permissions, and risk instead of relying only on the user’s network location.
4. What are the main benefits of Zero Trust?
Zero Trust can provide stronger access control, reduced security exposure, better cloud protection, improved visibility, and greater control over remote and third-party access.


